“One click. That’s all it takes. ‘It won’t happen to me’… until it actually does.”
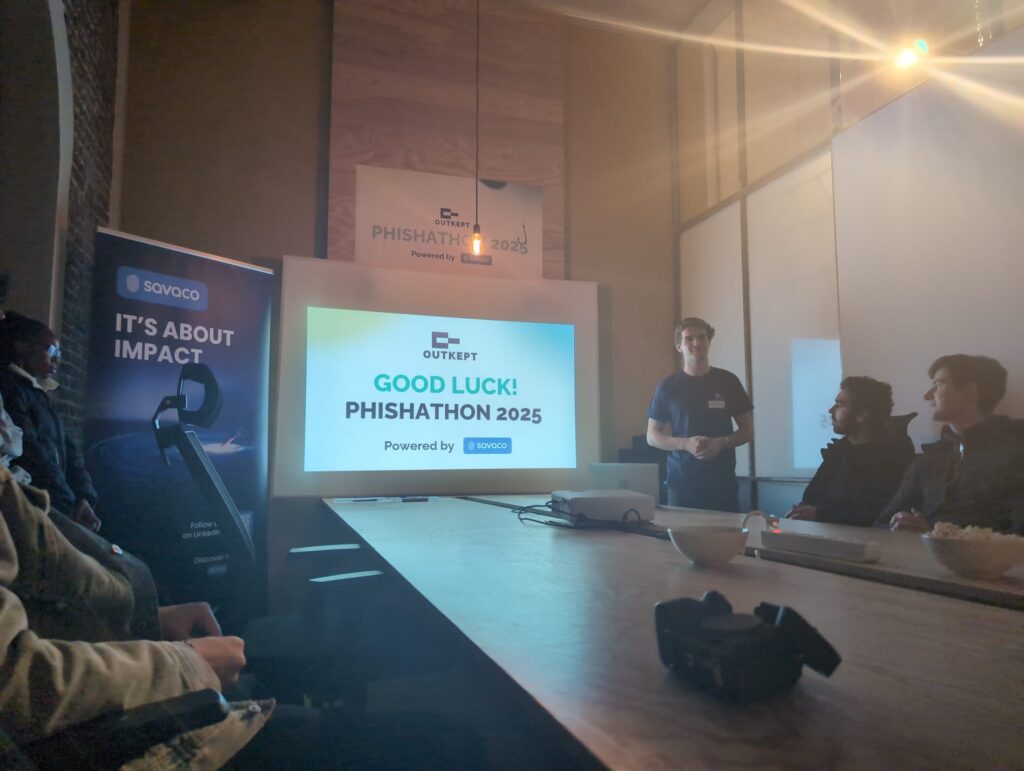
In the world of cybersecurity, we spend a massive amount of time building defenses, auditing frameworks, and analyzing risks from the perspective of the defender. But on November 6th, 2025, I got to flip the script. I attended the 2nd OutKept Phishathon, and it completely changed the trajectory of my cybersecurity journey.
The event, organized by Charles Staelens and brilliantly supported by Savaco and the OutKept team, was a grueling, exhilarating five-hour hacking marathon. The challenge? Put on the black hat for an evening and pretend to be the bad guys.
Deepfakes, Spear-Phishing, and Heavy Thinking
To effectively defend an organization against social engineering, you have to understand exactly how threat actors think, adapt, and exploit human psychology. The Phishathon pushed us to think outside the box with highly realistic, sophisticated scenarios:
- Spear-Phishing Hospitals: Crafting targeted, highly convincing pretexts aimed at healthcare environments—a sector where high stress and urgency make staff prime targets for attackers.
- Deepfaking Celebrities: Leveraging cutting-edge AI technology to generate artificial audio and video, demonstrating just how easily trust can be manipulated in the age of generative AI.
Between the intense brainpower required to build the perfect digital trap and the peak-quality pizza that kept us fueled, the energy in the room was electric. I walked away from the event with a massive appreciation for OutKept’s mission and a brand-new title: Ethical Phisher.
Turning Inspiration into Action: My Ethical Phishing Career Today
What started as a five-hour competition in November didn’t end when the event wrapped up. The Phishathon served as a massive catalyst for me. It made me realize that technical controls are only half the battle; human-centric security and continuous awareness training are where the real gaps lie.
Since that event, I have officially kicked off my career in ethical phishing. Today, I utilize the exact same psychological triggers and advanced techniques I experimented with at the Phishathon, but for good. By designing and executing controlled, simulated phishing campaigns, I help organizations:
- Identify weak points in their human firewall before actual threat actors do.
- Gather real-world data to drive impactful security awareness training.
- Bridge the gap between rigid GRC compliance policies and actual day-to-day human behavior.
A massive thank you once again to Charles Staelens, Savaco, and OutKept for putting together an event that was not only incredibly fun but genuinely career-defining.
If you think your organization is completely immune to social engineering, remember: it only takes one click. Let’s make sure that click happens during a simulation, not a real breach. See you at the next Phishathon! 🎣